Security Engineer Resume Example (2026)
By FindAJobAI team Updated How we built this page
Security hiring managers look for evidence that risk went down because of you: threats detected faster, vulnerabilities fixed sooner, audits passed, incidents contained. A security engineer resume full of acronyms but short on outcomes is hard to tell apart from the next one.
The example below is a cybersecurity engineer with seven years, from a security operations center to cloud security and detection engineering at a SaaS company. It names frameworks only where they did work under them, and keeps incident details at a level that's safe to share.
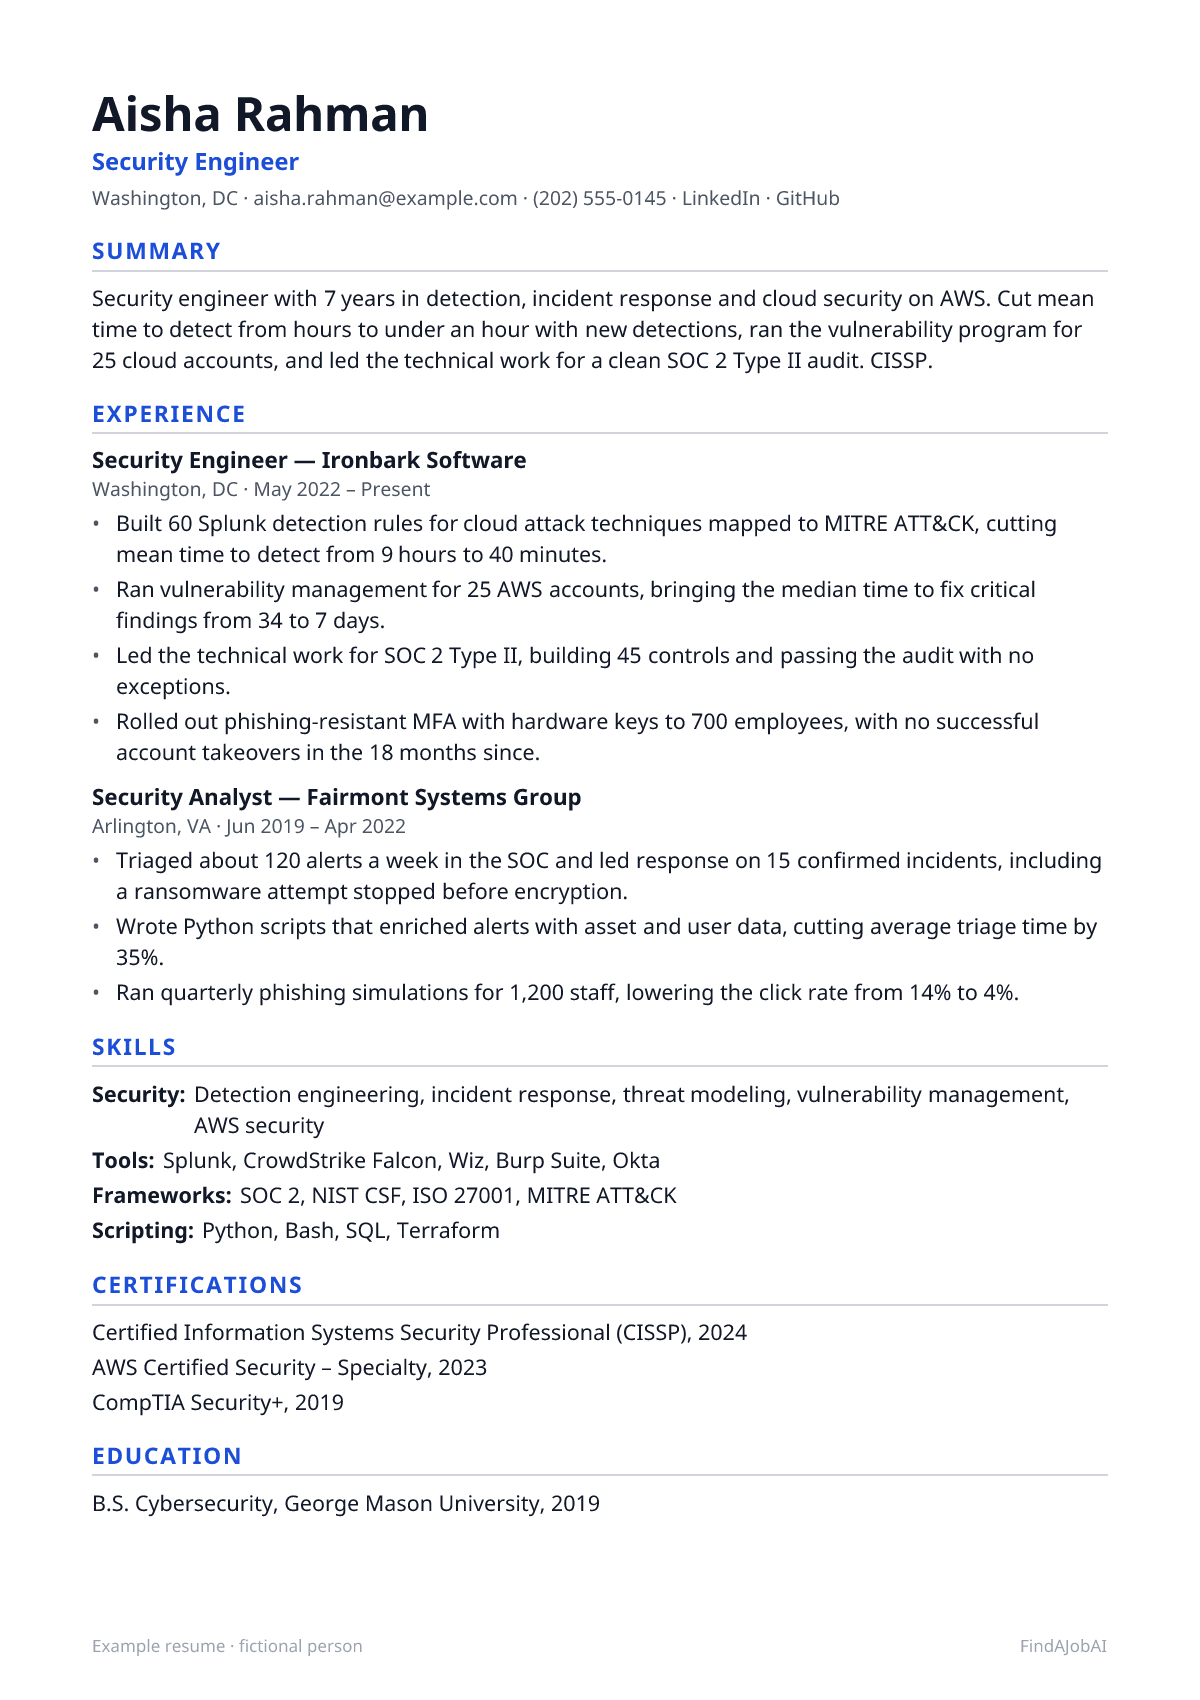
Security Engineer resume template
This example as a one-page template: one column, standard headings and plain text, the format applicant tracking systems read most reliably.
After you sign up, Create my CV builds your own resume in this same one-column layout, from your real experience.
Mid-level security engineer resume example
A complete one-page example for a fictional security engineer: every bullet pairs an action with what changed because of it.
Example resume · fictional person
Aisha Rahman
Security Engineer
Washington, DC · [email protected] · (202) 555-0145 · LinkedIn · GitHub
Summary
Security engineer with 7 years in detection, incident response and cloud security on AWS. Cut mean time to detect from hours to under an hour with new detections, ran the vulnerability program for 25 cloud accounts, and led the technical work for a clean SOC 2 Type II audit. CISSP.
Experience
Security Engineer, Ironbark Software
Washington, DC · May 2022 – Present
- Built 60 Splunk detection rules for cloud attack techniques mapped to MITRE ATT&CK, cutting mean time to detect from 9 hours to 40 minutes.
- Ran vulnerability management for 25 AWS accounts, bringing the median time to fix critical findings from 34 to 7 days.
- Led the technical work for SOC 2 Type II, building 45 controls and passing the audit with no exceptions.
- Rolled out phishing-resistant MFA with hardware keys to 700 employees, with no successful account takeovers in the 18 months since.
Security Analyst, Fairmont Systems Group
Arlington, VA · Jun 2019 – Apr 2022
- Triaged about 120 alerts a week in the SOC and led response on 15 confirmed incidents, including a ransomware attempt stopped before encryption.
- Wrote Python scripts that enriched alerts with asset and user data, cutting average triage time by 35%.
- Ran quarterly phishing simulations for 1,200 staff, lowering the click rate from 14% to 4%.
Skills
- Security: Detection engineering, incident response, threat modeling, vulnerability management, AWS security
- Tools: Splunk, CrowdStrike Falcon, Wiz, Burp Suite, Okta
- Frameworks: SOC 2, NIST CSF, ISO 27001, MITRE ATT&CK
- Scripting: Python, Bash, SQL, Terraform
Certifications
- Certified Information Systems Security Professional (CISSP), 2024
- AWS Certified Security – Specialty, 2023
- CompTIA Security+, 2019
Education
- B.S. Cybersecurity, George Mason University, 2019
Fictional example by the FindAJobAI team: the person, employers and numbers are invented. Keep the structure; use your own work and numbers you can explain in an interview.
Entry-level security engineer resume example
A junior engineer in vulnerability management with an application security internship behind him. Findings are counted and aged, the scanners are named, and a competitions section stands in for experience the way projects do in other fields.
Entry-level example resume · fictional person
Darius Freeman
Security Engineer
Baltimore, MD · [email protected] · (410) 555-0173 · LinkedIn · GitHub
Summary
Junior security engineer with a B.S. in Cybersecurity, an application security internship and a year in vulnerability management. Runs scanners and works the findings through with developers, reviews pull requests for common flaws, and writes Python and Bash. Security+ certified.
Experience
Security Engineer I, Vulnerability Management, Chesapeake Software
Baltimore, MD · Sep 2025 – Present
- Run weekly Tenable and Trivy scans across 900 hosts and 140 container images, routing findings to owning teams in Jira.
- Cut the median age of high-severity findings from 45 to 18 days by adding owners, deadlines and a weekly report.
- Wrote a Python script that merges duplicate findings across scanners, shrinking the ticket queue by a third.
Application Security Intern, Harbor Point Financial
Baltimore, MD · May 2025 – Aug 2025
- Reviewed 60 pull requests for injection, authentication and secrets issues, finding 2 high-severity flaws before release.
- Added Semgrep rules to CI for 8 repositories, blocking hard-coded secrets at merge.
Skills
- Security: Vulnerability management, secure code review, OWASP Top 10, alert triage
- Tools: Tenable, Trivy, Semgrep, Burp Suite, Splunk
- Scripting: Python, Bash, SQL
Certifications
- CompTIA Security+, 2024
Competitions
- Collegiate cyber defense competition, regional finalist, 2025
- University CTF team captain; placed 41st of 900 teams in a national event, 2024
Education
- B.S. Cybersecurity, University of Maryland, Baltimore County, 2025
Senior security engineer resume example
A manager of a security team at a regulated SaaS company. The clearance sits at the top, where government-facing employers look for it, and the bullets measure the program: response times, controls implemented, the age of open findings.
Senior example resume · fictional person
Ingrid Halvorsen
Security Engineering Manager
Arlington, VA · [email protected] · (571) 555-0177 · LinkedIn
Security clearance
- Secret, active
Summary
Security engineering manager with 14 years across incident response, cloud and application security, leading 7 engineers at a 2,000-person SaaS company. Built the detection and response program, brought critical findings older than 30 days to zero, and led the security work for FedRAMP Moderate and ISO 27001.
Experience
Security Engineering Manager, Potomac Cloud Systems
Arlington, VA · Jan 2021 – Present
- Lead 7 engineers across detection, cloud security and application security for a SaaS platform on AWS.
- Built 24/7 detection and response with a managed partner and 150 in-house detections, cutting mean time to respond from 6 hours to 35 minutes.
- Led the security work for FedRAMP Moderate, implementing 320 controls and passing the assessment on the first attempt.
- Ran a vulnerability program that reached zero critical findings older than 30 days across 60 AWS accounts.
Senior Security Engineer, Liberty Health IT
Reston, VA · Mar 2016 – Dec 2020
- Led incident response on 40 confirmed incidents, including a credential-stuffing attack contained within 2 hours.
- Designed the cloud security baseline (guardrails, logging, IAM boundaries) for 25 AWS accounts.
- Started a security champions program with 20 developers, halving high-severity penetration test findings.
Security Analyst, Federal Systems Group
Herndon, VA · Jun 2012 – Feb 2016
- Monitored and triaged alerts for 3 federal agency clients in a 24/7 security operations center.
Skills
- Programs: Detection and response, vulnerability management, cloud security, application security, security architecture
- Frameworks: FedRAMP, ISO 27001, SOC 2, NIST 800-53, MITRE ATT&CK
- Tools: Splunk, CrowdStrike Falcon, Wiz, AWS Security Hub, Okta
- Leadership: Hiring, security budgets, risk reporting to the board
Certifications
- Certified Information Systems Security Professional (CISSP), 2016
- GIAC Certified Incident Handler (GCIH), 2018
Education
- M.S. Information Security, Johns Hopkins University, 2015
- B.S. Computer Science, Virginia Tech, 2012
How to write a security engineer resume
Five steps, in the order a recruiter reads the page. The format around them stays plain for every job: one column, standard headings, newest role first.
Header: name, target title and links
Use the title from the ad (Security Engineer, Cybersecurity Engineer, Detection Engineer, Cloud Security Engineer). If you hold a clearance and the role needs one, put its level and status right under your name.
Summary: what you do and your best proof
Name your area (detection, cloud, application security or governance), the environment you protect and one measurable reduction in risk, such as faster detection or fewer open critical findings.
Experience: newest first, a result in every bullet
Measure what changed: time to detect or contain, findings closed, controls passed, incidents stopped. Keep details general enough that no employer, customer or internal system can be identified.
Skills: grouped, in the ad's words
Group domains, tools, frameworks and scripting. Write tools as product names (Splunk, CrowdStrike, Wiz) and frameworks by their standard names.
Education and certifications
Degree and year, then certifications in full with the abbreviation and year. Competitions, CTF results and published research can go in a short extra section.
Skills to put on a security engineer resume
Hard skills are the tools and methods of the job; soft skills are how you work with people. Each comes with one way to prove it, because a skill named only in a list counts for little. Add the ones you really have.
Hard skills
- SIEM and detection engineering
- Name the SIEM and count the detections you wrote, with time to detect.
- Incident response
- Give the incidents you handled and time to contain, without sensitive detail.
- Vulnerability management
- Show finding counts and fix times before and after your work.
- Cloud security
- Name the provider and the controls you built: guardrails, logging, IAM boundaries.
- Application security
- Mention code reviews or SAST and DAST tools, and the flaws caught before release.
- Identity and access management
- Describe MFA, SSO or least-privilege work and how many people or systems it covered.
- Network security
- Mention segmentation, firewalls or zero-trust access, with the systems covered.
- Threat modeling
- Name a system you modeled and the design change it led to.
- Compliance frameworks
- Say which framework (SOC 2, ISO 27001, PCI DSS, FedRAMP) and which part you owned.
- Security automation
- Show Python or Bash that sped up triage or response.
- Endpoint detection
- Name the EDR tool and the size of the fleet you covered.
- Penetration testing
- Mention tests you ran or managed and how the findings were fixed.
Soft skills
- Discretion
- Describe incidents in safe, general terms; doing so is itself a signal of judgment.
- Influence
- Show a control developers adopted because you made it easy to use.
- Risk communication
- Mention a risk you explained to leadership and the decision it led to.
- Curiosity
- Describe a threat you hunted for without an alert prompting you.
- Composure
- Mention leading the response during a live incident.
- Teaching
- Count the developers or staff you trained and what changed afterwards.
What employers ask for in security engineer job ads
The skills named most often in the 504 newest security engineer job ads we track (out of 2,841 live postings), as the share of ads that mention each:
- 1Incident management40%
- 2AWS35%
- 3Python35%
- 4Cloud security30%
- 5Azure28%
- 6Vulnerability management27%
- 7NIST26%
- 8Auditing24%
Certifications mentioned most: CISSP (26%). Many ads list them as a plus, not a requirement.
Add only the ones you really have, in Skills and in a bullet that shows how you used them. The full list is on the Security Engineer resume keywords page.
From live job ads · computed November 2, 2026 · refreshed daily
Security Engineer resume bullet examples: weak vs strong
The same work, written two ways. The strong version names the tool, the scope and a result; the numbers are examples, yours must be real.
Weak: Monitored security alerts.
Strong: Tuned 40 noisy SIEM rules and added asset context, cutting false positives by 65% so analysts could clear every high-severity alert the same day.
Shows detection judgment and its effect on the team.
Weak: Performed vulnerability scans.
Strong: Moved vulnerability scanning into CI with Trivy and set fix deadlines by severity, cutting open critical findings from 210 to 12 in two quarters.
Turns scanning into a program with measurable results.
Weak: Responded to security incidents.
Strong: Contained a leaked CI token within 25 minutes, rotated 80 credentials and led the postmortem that moved CI to short-lived OIDC credentials.
Speed, scope and the lasting fix.
Weak: Helped with compliance.
Strong: Mapped 120 SOC 2 and ISO 27001 controls to automated evidence in Drata, cutting audit preparation from 6 weeks to 10 days.
Compliance work with the time it saved, naming both frameworks.
Weak: Did penetration testing.
Strong: Tested 6 web app releases with Burp Suite before launch, finding 3 high-severity authorization flaws that were fixed before release.
Method, scope and findings, without overstating the role.
Weak: Promoted security awareness.
Strong: Wrote a secure code review checklist and ran 8 workshops for 90 developers, after which injection findings in pen tests fell from 7 to 1.
Training measured by what changed in the code.
15 more security engineer resume bullet examples
Grouped by area of the job, so you can find the ones closest to your work. Keep the shape (action, scope, result) and replace the invented numbers with your own.
Detection and response
- Wrote 35 detections for identity attacks in Microsoft Sentinel, catching 2 compromised accounts within an hour of first misuse.
- Built automated playbooks that isolate an endpoint and reset credentials on high-confidence alerts, cutting containment from 50 minutes to 4.
- Hunted for persistence techniques across 3,000 endpoints in CrowdStrike, finding and removing 6 unauthorized remote-access tools.
- Ran 4 tabletop exercises with engineering and legal, feeding 15 changes into the incident response plan.
Cloud and infrastructure security
- Enabled organization-wide CloudTrail and GuardDuty across 40 AWS accounts, with alerts routed to the security operations team.
- Removed 1,200 unused IAM keys and roles and enforced short-lived credentials, cutting standing access by 80%.
- Deployed Wiz across 3 clouds and fixed 90 critical misconfigurations in the first quarter, including 4 public storage buckets.
- Rolled out zero-trust access for 50 internal apps, retiring the VPN for 1,500 employees.
Application security
- Added SAST, dependency and secret scanning to 120 repositories, blocking 300 vulnerable merges in a year.
- Threat-modeled a new payments feature with its team and changed the token design before any code was written.
- Ran a bug bounty program with a $60,000 annual budget, triaging 400 reports and paying out on 45 valid findings.
Governance and awareness
- Mapped 90 ISO 27001 controls to evidence and owners, reaching certification in 9 months.
- Rewrote 12 security policies in plain language, halving policy questions sent to the security team.
- Built role-based security training for 800 staff, lifting the share of phishing tests reported from 20% to 65%.
- Assessed 70 vendors with tiered reviews, rejecting 3 that failed basic data protection requirements.
Security Engineer resume summary examples
Two or three lines on what you do and your strongest proof. Start from the one closest to your level and use your own facts.
Security analyst with a Security+ certificate and 18 months in a SOC, triaging alerts in Splunk and CrowdStrike. Wrote Python scripts that cut triage time by a third. Building toward cloud security and detection engineering.
Security engineer with 5 years in cloud security and detection on AWS. Built the detection program for a fintech, cut critical vulnerability fix times from weeks to days, and led two SOC 2 audits.
Senior security engineer with 11 years across incident response, application security and cloud security, leading a team of 4. Built the security program for a 600-person SaaS company from the first hire through ISO 27001 certification.
Common security engineer resume mistakes
Each one is easy to make and quick to fix before you apply.
Acronym soup
A line of twenty acronyms hides what you did. Name the frameworks and tools you worked with inside bullets about results.
Sharing too much about incidents
Customer names, internal hostnames and attack specifics don't belong on a resume. Describe incidents by type, scale and outcome.
No measure of risk reduced
Security work is judged by what became safer. Add detection times, finding counts or audit outcomes.
Certifications as the whole story
Certificates open doors, but hiring managers read for hands-on work. Put that evidence in the bullets.
Overstating offensive skills
Listing penetration testing after one course invites a practical test. Claim the depth you have, and show labs or CTFs for the rest.
ATS tips for a security engineer resume
Applicant tracking systems turn your file into text that recruiters search, mostly for the skills and titles in the ad. They rarely reject a resume on their own; one that parses badly or misses the ad's words just doesn't come up.
- List the frameworks you actually worked under (SOC 2, ISO 27001, NIST CSF, PCI DSS) and what you did for each, not every acronym you know.
- Write certifications in full with the abbreviation, such as Certified Information Systems Security Professional (CISSP); both forms get searched.
- Name tools by product (Splunk, CrowdStrike, Wiz, Burp Suite); security recruiters often search for a specific stack.
- Keep incident details at a level you're allowed to share: no customer names or internal system names.
- If the role needs a security clearance and you hold one, state its level and status near the top.
For the format itself, run the free ATS resume checklist.
Everything for Security Engineers
- Security Engineer jobs2,841 open roles, updated hourly
- Security Engineer salary in the United StatesAdvertised pay in real job ads
- Security Engineer cover letter examplesThree example letters and a short email version
- Security Engineer interview questions30 questions with sample answers
- Security Engineer resume keywordsThe skills job ads ask for most
- Security Engineer job descriptionDuties, skills and requirements
- How to tailor your resume without lying
Other resume examples
Security Engineer resume FAQ
Which certifications matter most on a security engineer resume?
It depends on the role: Security+ for entry-level and government jobs, CISSP for senior and management-track roles, and cloud security certifications for cloud-heavy teams. Hands-on results still carry more weight than the list.
How much detail can I give about security incidents?
Give your role, the type of incident, how fast it was contained and the fix, but nothing confidential. "Contained a credential-stuffing attack within an hour" shows skill without breaking any agreement.
Should I list CTFs or bug bounties?
Yes, in a short Projects or Achievements section, especially early in your career. Rankings, accepted reports and write-ups show hands-on skill an employer can check.
How we built this page
The FindAJobAI team wrote the three example resumes, the bullets, the skills and the advice for security engineer roles. The people, employers and numbers in the examples are invented; the structure, the tools and the way each bullet is built are the parts to copy.
The live skills section is based on 504 security engineer job ads analysed, the newest we track, with the same deterministic skill matcher as our in-demand skills report: no AI model reads the postings. It was last computed on November 2, 2026 and refreshes daily.
Last reviewed on November 1, 2026.