Penetration Tester Resume Example (2026)
By FindAJobAI team Updated How we built this page
Penetration tester job ads usually list the same tools: Burp Suite, Metasploit, Nmap, maybe Cobalt Strike for red team work. What makes a resume stand out is evidence that your findings mattered, not a longer tool list. A penetration tester resume should show the method, the access gained and what the client did about it.
The example below has four years split between a boutique security consultancy and client-facing fintech and healthcare work. Each bullet names the technique, the finding and either the exposure it prevented or the fix it drove, instead of counting tests run.
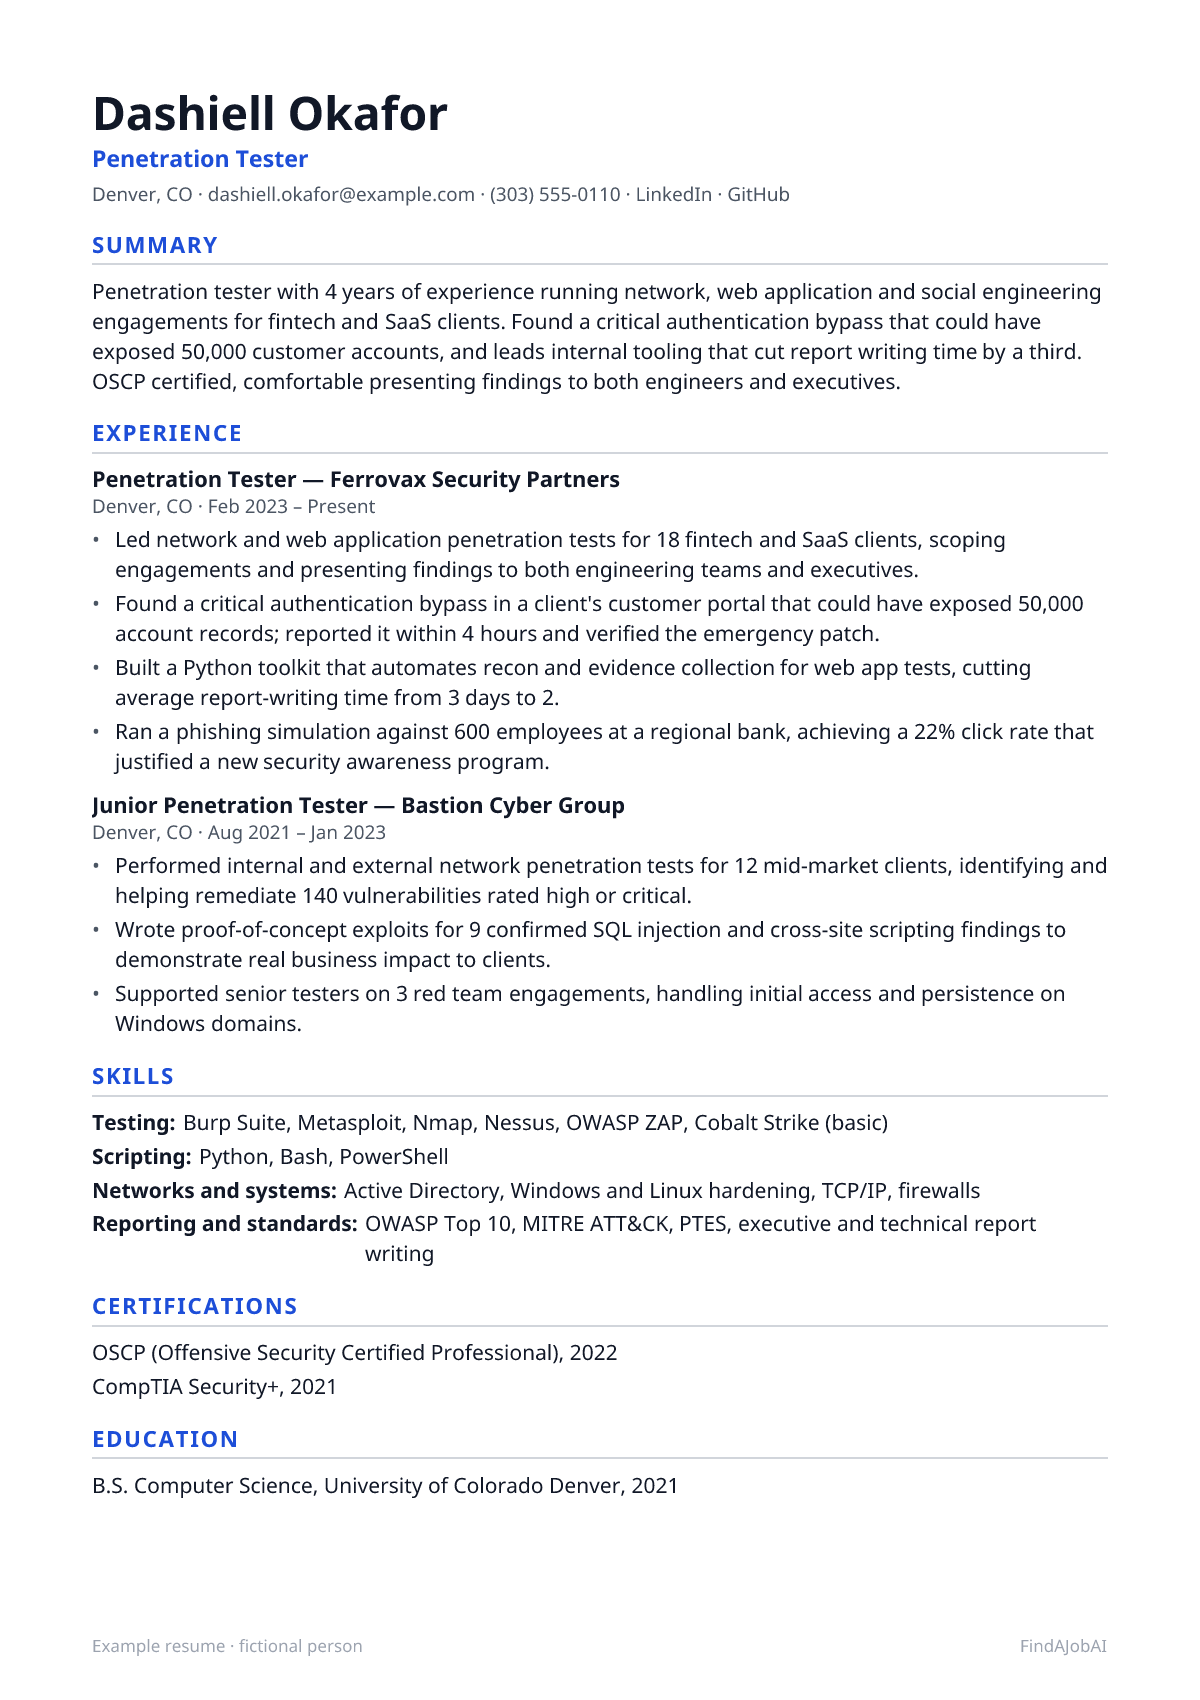
Penetration Tester resume template
This example as a one-page template: one column, standard headings and plain text, the format applicant tracking systems read most reliably.
After you sign up, Create my CV builds your own resume in this same one-column layout, from your real experience.
Mid-level penetration tester resume example
A complete one-page example for a fictional penetration tester: every bullet pairs an action with what changed because of it.
Example resume · fictional person
Dashiell Okafor
Penetration Tester
Denver, CO · [email protected] · (303) 555-0110 · LinkedIn · GitHub
Summary
Penetration tester with 4 years of experience running network, web application and social engineering engagements for fintech and SaaS clients. Found a critical authentication bypass that could have exposed 50,000 customer accounts, and leads internal tooling that cut report writing time by a third. OSCP certified, comfortable presenting findings to both engineers and executives.
Experience
Penetration Tester, Ferrovax Security Partners
Denver, CO · Feb 2023 – Present
- Led network and web application penetration tests for 18 fintech and SaaS clients, scoping engagements and presenting findings to both engineering teams and executives.
- Found a critical authentication bypass in a client's customer portal that could have exposed 50,000 account records; reported it within 4 hours and verified the emergency patch.
- Built a Python toolkit that automates recon and evidence collection for web app tests, cutting average report-writing time from 3 days to 2.
- Ran a phishing simulation against 600 employees at a regional bank, achieving a 22% click rate that justified a new security awareness program.
Junior Penetration Tester, Bastion Cyber Group
Denver, CO · Aug 2021 – Jan 2023
- Performed internal and external network penetration tests for 12 mid-market clients, identifying and helping remediate 140 vulnerabilities rated high or critical.
- Wrote proof-of-concept exploits for 9 confirmed SQL injection and cross-site scripting findings to demonstrate real business impact to clients.
- Supported senior testers on 3 red team engagements, handling initial access and persistence on Windows domains.
Skills
- Testing: Burp Suite, Metasploit, Nmap, Nessus, OWASP ZAP, Cobalt Strike (basic)
- Scripting: Python, Bash, PowerShell
- Networks and systems: Active Directory, Windows and Linux hardening, TCP/IP, firewalls
- Reporting and standards: OWASP Top 10, MITRE ATT&CK, PTES, executive and technical report writing
Certifications
- OSCP (Offensive Security Certified Professional), 2022
- CompTIA Security+, 2021
Education
- B.S. Computer Science, University of Colorado Denver, 2021
Fictional example by the FindAJobAI team: the person, employers and numbers are invented. Keep the structure; use your own work and numbers you can explain in an interview.
Entry-level penetration tester resume example
A career-changer with a cybersecurity bootcamp and a help desk background, one year into testing. Home lab and CTF work fill in for engagement history, each one ending in a specific exploit or rank rather than hours logged.
Entry-level example resume · fictional person
Sage Gunnarsson
Penetration Tester
Tempe, AZ · [email protected] · (480) 555-0179 · LinkedIn · GitHub · Portfolio
Summary
Entry-level penetration tester with the eJPT, a cybersecurity bootcamp certificate, and 3 years of IT help desk experience. Ranked in the top 5% of 2,000 users on Hack The Box and completed 40 TryHackMe rooms covering Active Directory and web exploitation. Documents findings clearly for readers without a security background.
Education
- B.A. Information Technology, Arizona State University, 2021
Experience
IT Support Specialist, Sonoran Desert Credit Union
Tempe, AZ · Jun 2022 – Present
- Resolved an average of 25 tickets a day covering account access, VPN and endpoint issues for 300 employees, while studying for the eJPT on evenings and weekends.
- Flagged a phishing email that had already reached 60 inboxes, helping IT pull it from every mailbox within 20 minutes and prompting a staff-wide warning.
- Hardened 15 branch workstation images by closing unused ports and disabling legacy protocols, following guidance from the credit union's security team.
Cybersecurity Bootcamp, Capstone Project, Desert Ridge Cyber Academy
Tempe, AZ · Jan 2024 – May 2024
- Compromised a 6-machine lab network end to end, escalating from a public-facing web app to full domain admin and documenting every step in a client-style report.
- Presented findings to a panel of 3 working penetration testers, who scored the report among the top 4 of 22 submissions.
Skills
- Testing: Nmap, Burp Suite, Metasploit (basic), Wireshark, Hydra
- Scripting: Python, Bash
- Systems: Active Directory basics, Windows and Linux command line, TCP/IP
Certifications
- eJPT (eLearnSecurity Junior Penetration Tester), 2024
- CompTIA Security+, 2023
Labs and Competitions
- Hack the Box: ranked in the top 5% of 2,000 active users; rooted 45 machines across Windows and Linux.
- TryHackMe: completed 40 rooms, including the full Jr Penetration Tester path.
Senior penetration tester resume example
A team lead eight years in, now running red team engagements and managing testers. The bullets shift from individual findings to program-level impact: budgets protected, testers mentored and a methodology adopted firm-wide.
Senior example resume · fictional person
Rutherford Adeyemi
Lead Penetration Tester
Arlington, VA · [email protected] · (703) 555-0184 · LinkedIn
Summary
Lead penetration tester with 8 years across consulting and in-house security, running red team engagements for government contractors and a $2B retailer's payment systems. Manages 4 testers, owns the firm's engagement methodology, and has reported 3 findings that led to CVEs.
Experience
Lead Penetration Tester, Graywolf Security Consulting
Arlington, VA · Apr 2021 – Present
- Lead a team of 4 penetration testers across network, web application and red team engagements for government contractors and retail clients handling $2B in annual payment volume.
- Ran a 6-week red team engagement against a retailer's payment network, gaining domain admin through an unpatched print server and reaching the point-of-sale segment undetected for 11 days.
- Rewrote the firm's engagement methodology and report template, adopted across all 4 teams, cutting average delivery time from 3 weeks to 2.
- Reported 3 vulnerabilities in a widely used VPN appliance that were assigned CVEs, coordinating disclosure with the vendor over 90 days.
Senior Penetration Tester, Blackferry Cyber
Reston, VA · Jul 2017 – Mar 2021
- Ran 60+ network and web application engagements for mid-market and enterprise clients, mentoring 5 junior testers in exploit development and report writing.
- Found a privilege escalation flaw in a healthcare client's patient portal that exposed admin functions to standard users, rated critical and fixed within 48 hours.
- Built a Cobalt Strike and Active Directory attack-path training lab used to onboard every new hire on the team.
Penetration Tester, Ironwood Risk Advisors
Washington, DC · Aug 2014 – Jun 2017
- Performed external and internal network penetration tests for 25 clients in finance and healthcare, identifying over 500 findings across engagements.
- Co-authored the firm's first web application testing checklist, aligned to the OWASP Top 10 and still in use four years later.
Skills
- Testing: Cobalt Strike, Burp Suite, Metasploit, Nmap, BloodHound, Nessus
- Programming: Python, PowerShell, C (basic), Bash
- Leadership: Engagement scoping, mentoring testers, methodology and QA, client executive briefings
Certifications
- OSCP, 2016
- OSCE, 2019
- GPEN, 2020
Education
- B.S. Computer Engineering, Virginia Tech, 2014
How to write a penetration tester resume
Five steps, in the order a recruiter reads the page. The format around them stays plain for every job: one column, standard headings, newest role first.
Header: name, target title and links
Use the industry-standard title “Penetration Tester” even if your offer letter says Ethical Hacker or Offensive Security Engineer, and list the testing types you've run (network, web, mobile, red team) right under it.
Summary: what you do and your best proof
State your years of experience, the industries you've tested, and one finding or program result that shows impact. Skip lines like “skilled ethical hacker”; certifications and a real finding say it better.
Experience: newest first, a result in every bullet
Lead each bullet with the technique or target, then the access gained and what happened next: a fix, a disclosure or a new control. A vulnerability count tells a reader little; one exploit chain with its consequence tells them a lot.
Skills: grouped, in the ad's words
Group tools by testing type (web, network, red team) and list certifications by full name the first time, since OSCP and CEH are both searched by acronym and by name.
Education and certifications
A computer science or cybersecurity degree helps but matters less here than certifications and lab work. Without professional engagements, add a Labs and Competitions section naming your platform rank or specific machines compromised.
Skills to put on a penetration tester resume
Hard skills are the tools and methods of the job; soft skills are how you work with people. Each comes with one way to prove it, because a skill named only in a list counts for little. Add the ones you really have.
Hard skills
- Burp Suite
- Name a specific finding you made by intercepting or modifying requests, not just that you used the tool.
- Metasploit
- Mention the exploit module or payload you used and what access it gained.
- Nmap
- Pair a scan with what it revealed, such as an open service that led to a finding.
- Active Directory attacks
- Name a technique (Kerberoasting, pass-the-hash) and the privilege level you reached.
- Web application testing
- Reference the OWASP Top 10 category of a real finding, like broken access control or injection.
- Social engineering
- Give the campaign size, the click or response rate, and the control it led to.
- Python scripting
- Describe a tool or script you wrote and the time or step it saved during testing.
- Report writing
- Mention a template or structure change and how it changed client understanding or turnaround time.
- Vulnerability scanning (Nessus, Qualys)
- Say how you triaged scanner output, since raw scan counts mean little on their own.
- Cobalt Strike
- Use it only if you've run red team work, and name the detection or response it tested.
- Wireless testing
- Name the protocol or attack (WPA2 handshake capture, rogue AP) and what it exposed.
- Cloud security testing (AWS, Azure)
- Give the misconfiguration type you found, such as an open S3 bucket or over-permissioned role.
- Mobile application testing
- Note the platform and the kind of flaw, like insecure storage or weak API authentication.
Soft skills
- Clear technical writing
- Describe a report or template change and its effect on client questions or turnaround.
- Risk communication
- Give an example of translating a technical finding into business impact for an executive.
- Client management
- Mention how you scoped or briefed an engagement with a client-facing number, like attendee count.
- Mentoring
- Count the testers you trained and in what skill, such as exploit development.
- Ethics and discretion
- Reference handling sensitive findings responsibly, such as a disclosure timeline you followed.
- Curiosity
- Describe a finding that came from testing beyond the original scope or checklist.
- Time management
- Give the engagement length and how you kept testing and reporting on schedule.
Penetration Tester resume bullet examples: weak vs strong
The same work, written two ways. The strong version names the tool, the scope and a result; the numbers are examples, yours must be real.
Weak: Performed penetration tests.
Strong: Ran a black-box penetration test of a healthcare client's patient portal and found 6 high-severity flaws, including one that exposed lab results through a predictable URL parameter.
Names the target, the method and the real-world exposure.
Weak: Found vulnerabilities in web applications.
Strong: Chained a stored XSS with a missing CSRF token to demonstrate full account takeover on a retail client's checkout flow, included as the engagement's top finding.
Shows the exploit chain and its business weight, not just a vulnerability count.
Weak: Used Burp Suite and Metasploit.
Strong: Used Burp Suite to intercept and modify API requests, bypassing role-based access checks that let a standard user view 400 other customers' invoices.
Turns tool names into a specific access-control failure.
Weak: Wrote reports for clients.
Strong: Rewrote the firm's report template to separate business risk from technical detail, cutting client questions about findings by half in the following quarter.
Reporting skill shown through a process change and its effect on clients.
Weak: Tested network security.
Strong: Mapped a manufacturing client's flat internal network and showed that a compromised guest laptop could reach the SCADA segment in 3 hops.
Concrete path and consequence instead of a generic claim.
Weak: Conducted social engineering tests.
Strong: Ran a vishing campaign against 40 help desk staff and obtained password resets for 11 accounts, leading the client to add a callback verification step.
Specific numbers and the resulting security control.
15 more penetration tester resume bullet examples
Grouped by area of the job, so you can find the ones closest to your work. Keep the shape (action, scope, result) and replace the invented numbers with your own.
Web application testing
- Chained an IDOR with a weak session token to view 2,000 other users' order histories on an e-commerce client's account page.
- Found a SQL injection in a login form that returned full database access, verified safely and reported within 2 hours of discovery.
- Bypassed multi-factor authentication for a banking client by replaying a captured session cookie, exposing full access to 15,000 customer accounts.
- Tested 30 API endpoints for a fintech client and found 8 missing authorization checks that exposed other customers' account balances.
Network and infrastructure testing
- Pivoted from a compromised print server to the finance VLAN in 3 hops, demonstrating a path to payroll data on a flat internal network.
- Cracked 180 of 600 captured password hashes within 4 hours using a custom wordlist built from the client's public data.
- Identified an unpatched VPN appliance that let an unauthenticated attacker read internal configuration files on a network serving 2,000 employees, reported as critical.
- Used BloodHound to map an Active Directory domain of 1,200 accounts and found a path from a help desk account to domain admin in 4 steps.
Social engineering and red team
- Ran a phishing campaign against 350 employees that achieved an 18% click rate, leading the client to launch quarterly awareness training.
- Gained physical access to a data center by tailgating and a cloned badge, undetected for 25 minutes, prompting new visitor-escort rules.
- Called 20 help desk staff posing as a locked-out employee and obtained 6 password resets without identity verification.
- Maintained undetected access to a retail client's network for 9 days during a red team engagement, exfiltrating simulated customer data to test detection.
Reporting and program impact
- Rewrote finding severity criteria to match CVSS v3.1, aligning scoring across a 6-person testing team.
- Tracked remediation on 90 findings across 2 quarters, reporting 70% closed within the client's agreed SLA.
- Built a reusable report template with an executive summary and risk matrix, cutting client follow-up questions by 35%.
Penetration Tester resume summary examples
Two or three lines on what you do and your strongest proof. Start from the one closest to your level and use your own facts.
Entry-level penetration tester with the eJPT and a cybersecurity degree, including a capstone project that compromised a deliberately vulnerable lab network end to end. Comfortable with Nmap, Burp Suite and basic Metasploit use, and documents findings clearly for non-technical readers.
Penetration tester with 4 years testing web applications and internal networks for fintech and healthcare clients. Comfortable scoping engagements, chaining findings into realistic attack paths, and presenting risk in plain language to both engineers and executives.
Senior penetration tester and team lead with 9 years across consulting and in-house security, running red team engagements against a $2B retailer's payment systems and mentoring 4 junior testers in exploit development and report writing.
Common penetration tester resume mistakes
Each one is easy to make and quick to fix before you apply.
Listing tools without a finding attached
Burp Suite and Metasploit in Skills show what you can run; a bullet should show what you found with them and what it meant for the client.
Counting vulnerabilities instead of impact
"Found 50 vulnerabilities" says less than one finding described by its access and consequence. Pick your strongest finding per engagement and detail it.
Naming real client companies
Most engagements are under NDA. Describe the client by industry and size instead, and keep the focus on the technique and the result.
Burying certifications in a paragraph
List OSCP, CEH, GPEN and similar certifications in their own line with the full name, since both recruiters and ATS systems search for them directly.
Vague red team bullets with no detection outcome
State how long access lasted and whether the client's team detected it, since that is usually the point of the exercise.
ATS tips for a penetration tester resume
Applicant tracking systems turn your file into text that recruiters search, mostly for the skills and titles in the ad. They rarely reject a resume on their own; one that parses badly or misses the ad's words just doesn't come up.
- Name the testing types you've run (network, web app, mobile, red team, social engineering); ads often ask for a specific mix.
- List certifications in full the first time (OSCP, CEH) since some ATS systems and recruiters search by the acronym and the spelled-out name.
- Describe findings by their real-world impact, not a vulnerability count: what could an attacker actually do.
- Name the tools you used for a specific finding, not just a tool list in Skills.
- If you hold a clearance or have worked with regulated clients (HIPAA, PCI-DSS, SOC 2), say so; many client contracts require it.
For the format itself, run the free ATS resume checklist.
Everything for Penetration Testers
- Penetration Tester cover letter examplesThree example letters and a short email version
- Penetration Tester interview questions30 questions with sample answers
- Penetration Tester job descriptionDuties, skills and requirements
- How to tailor your resume without lying
Other resume examples
Penetration Tester resume FAQ
What certifications matter most on a penetration tester resume?
OSCP carries the most weight because it is hands-on, followed by CEH and GPEN for recognition, and Security+ as an entry point. List the full name with the acronym the first time.
How do I write a penetration tester resume with no professional experience?
Lean on home lab work, capture-the-flag competitions and platforms like Hack The Box or TryHackMe, described as specific boxes or ranks rather than hours spent, plus any eJPT or similar certification.
Should a penetration tester resume include specific client names?
Usually not, since most engagements are under NDA. Describe the client by industry and size instead, and focus the bullet on the finding and its impact.
How technical should penetration tester resume bullets be?
Technical enough that another tester recognizes the method, but plain enough that a hiring manager without security depth understands the risk; naming the impact does both.
How we built this page
The FindAJobAI team wrote the three example resumes, the bullets, the skills and the advice for penetration tester roles. The people, employers and numbers in the examples are invented; the structure, the tools and the way each bullet is built are the parts to copy.
Once we track enough live penetration tester job ads, this page also shows the skills they ask for most, counted the same way as our in-demand skills report.
Last reviewed on November 1, 2026.